Trust you can read up on.
How ETSpilot handles your project and your data – technically, organisationally and contractually. For users, data protection officers and purchasing.
Where your data goes – and where it doesn't.
The AddIn only reads the parts of the project that the current task requires. Locked data types never leave your computer.
What is transmitted
Excerpts for the task: building structure, device and address names, parameter names, your message.
What you can lock
Per project, e.g. security keys, serial numbers, parameters or customer data – they are never sent.
What never happens
No training with your data, no analysis, no sharing, no advertising, no tracking.
Nothing happens without you.
The most important security feature is the one that protects your project: approval, backup and traceability.
Approval
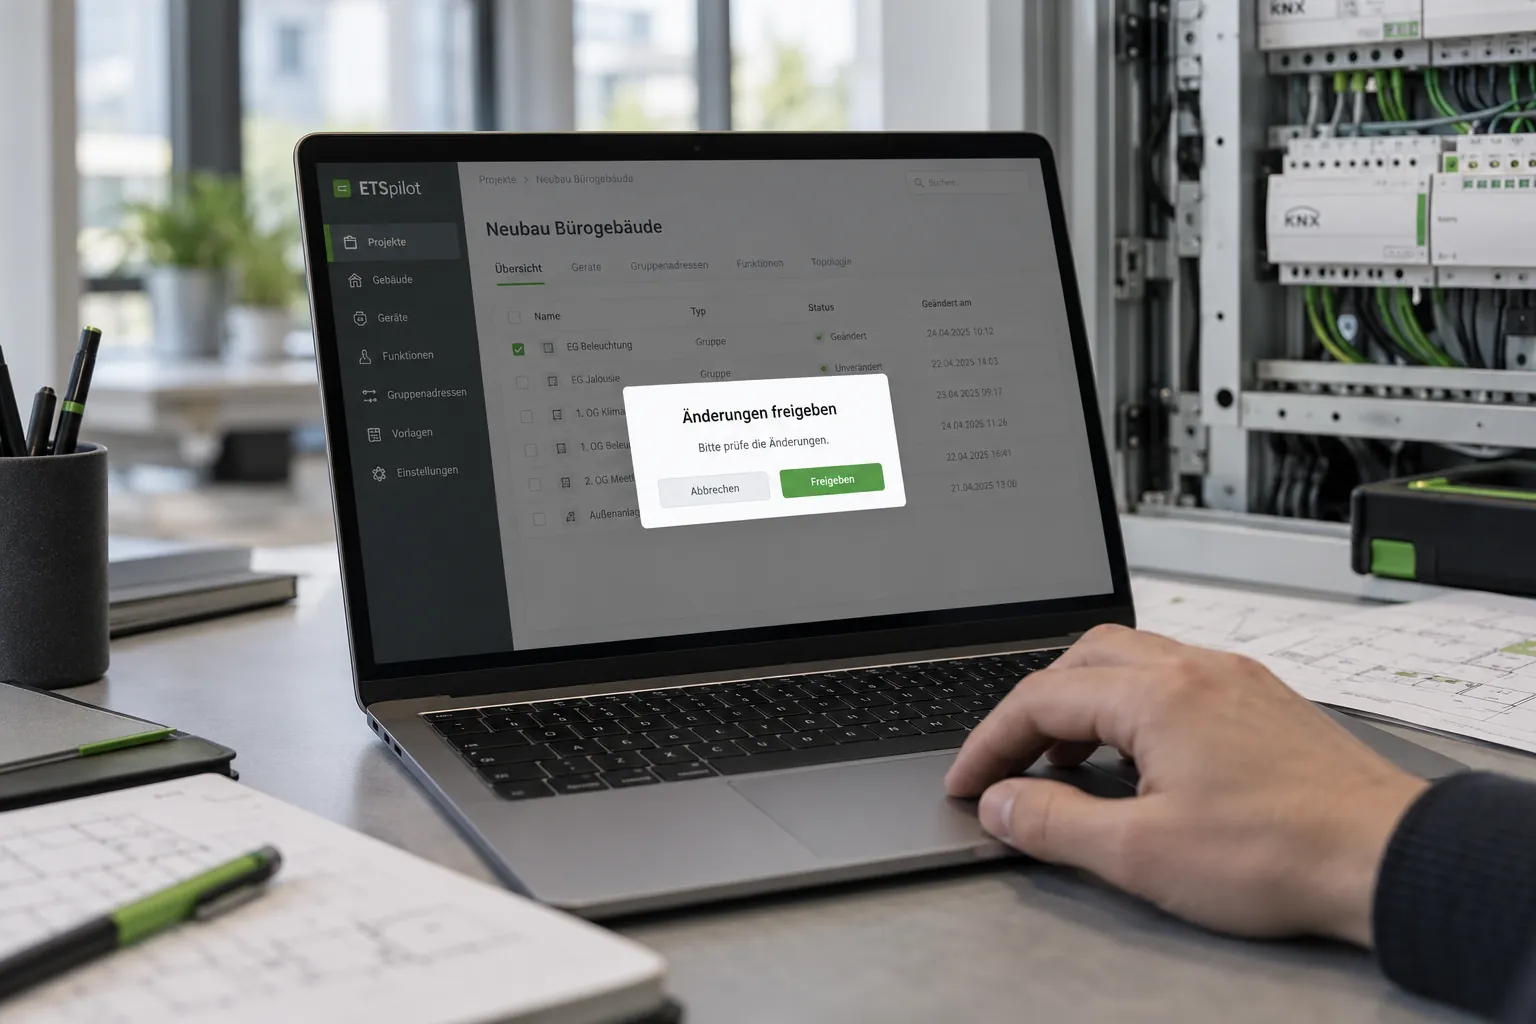
Every writing action is presented in plain language – individually or for the session.
Project backup
Automatically before the first change, optionally before every critical action.
Log
Every change carried out is traceable in the chat and in the report.
Ask mode
Read and explain only – for training, review and cautious first steps.
Honestly described.
Summary of the measures. The complete annex to the data processing agreement is available under “Documents”.
| Area | Measure |
|---|---|
| Transport | TLS for portal, interfaces, remote control and website. Requests between AddIn and server are additionally encrypted at application level with AES-256 (CBC + HMAC-SHA256). |
| Stored data | API keys and uploaded documents encrypted with AES-256-GCM. Chat histories and project data in the server database in Germany. |
| Sign-in | One-time code by e-mail instead of a password; sessions stored only as a hash. |
| Server access | SSH key only, one single operating user. From outside only ports 22, 80 and 443 are reachable – doubly secured by security group and server firewall. |
| Permissions | Administrators cannot see other users' chat histories or documents in the portal. |
| Logging | Technical logs without content, 30 days. A full diagnostic log is switched off and only activated temporarily for troubleshooting (deleted after 14 days). |
| Backup | Daily backup of the storage volume, stored separately, 14 days retention. |
| Incidents | Documented emergency and data breach process with reporting channels according to Art. 33/34 GDPR. |
| Data centre | STACKIT (Schwarz Group) in Germany; according to the provider certified to ISO 27001 and with BSI C5 attestation. |
What we store and for how long.
You can request information, export and deletion yourself in the portal at any time – without a support request.
| Data | Purpose | Retention period |
|---|---|---|
| E-mail address | Sign-in, account management | until the account is deleted |
| API key | Forwarding to your AI provider | until you delete it, encrypted |
| Chat histories | Answering your requests | automatically 3 months after last use |
| Planning documents | Searchability by the assistant | until you delete them, encrypted |
| Usage data | Billing, abuse detection | 400 days |
| Technical logs | Secure operation, troubleshooting | 30 days |
| Backups | Recovery | 14 days |
Who is involved in processing.
We announce changes in advance. The AI provider is not one of our subprocessors: you conclude the contract yourself and store your key.
| Company | Service | Location | Basis |
|---|---|---|---|
| STACKIT Schwarz Digits Cloud GmbH & Co. KG | Hosting of server and database | Germany | DPA 2.4.2 |
| STRATO GmbH | Sending sign-in codes and system e-mails | Germany | DPA 3.6 |
| Microsoft Ireland | Support mailbox | EU | Microsoft DPA |
| Let's Encrypt (ISRG) | TLS certificates – domain names only | USA | no personal data |
 approx. 3 min
Control & data protection
Approval, backup and data locks in three minutes.
Watch videoEverything for your review.
The documents are updated continuously. You can also conclude and archive the data processing agreement in the portal.
The questions you ask.
We answer further questions directly – write to us via the contact form with the subject “Data protection”.
Who is the controller, who is the processor?
We are the controller for account, usage data and website. We process content from your ETS projects on behalf of the user; the data processing agreement covers this.
Is data transferred to third countries?
Our server is located in Germany. A transfer to the USA only occurs if the user chooses a US provider (Anthropic, OpenAI) – under their own contract. With Azure, an EU region can be selected.
Is project data used for training?
No, not by us. The API terms of the supported providers exclude training with API data by default.
How can personal data be avoided?
With the data locks per project (e.g. customer data, serial numbers) and by keeping projects free of personal names.
Is a data protection impact assessment required?
We provide our threshold assessment on request. As the controller, you make the assessment for your use case.